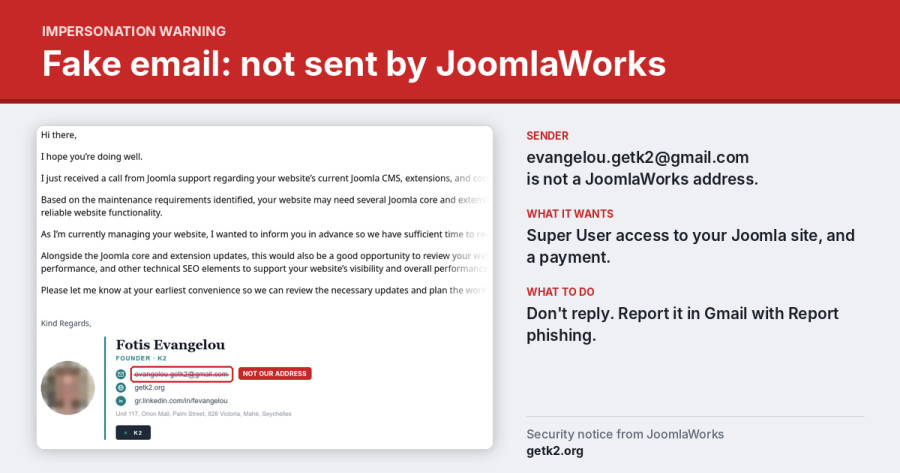
Since 14 October 2026, Joomla site owners have been receiving unsolicited emails that use Fotis Evangelou's name, a link to getk2.org and his public LinkedIn profile, together with a photograph of a different person. Several clients of JoomlaWorks and members of the Joomla community have forwarded these messages to us.
Their purpose is to obtain administrator access to the recipient's website and a payment for services that will not be delivered.
If you have received one of these emails, do not reply and do not create any user account.
This notice describes the messages, explains how to verify genuine correspondence from JoomlaWorks, and sets out the steps to take if you have already responded.
Description of the messages
The initial message carries the subject line "Important: Joomla Website Updates and Technical SEO Optimization Before October 25".
The message states that:
-
"Joomla support" contacted the sender by telephone regarding the recipient's Joomla installation, extensions and configuration.
-
The website requires core and extension updates before 25 October.
-
The sender is "currently managing" the recipient's website.
-
A review of the website's SEO configuration and technical optimisation should be carried out at the same time.
The signature includes Fotis Evangelou's name, the title "Founder · K2", links to getk2.org and to his LinkedIn profile, a postal address and a profile photograph. The photograph does not depict Fotis Evangelou.
None of these statements are accurate. Joomla is a volunteer-run open source project. It has no support service that contacts developers about third-party websites, and there is no Joomla deadline on 25 October. Replies to the address trigger an automatic response that repeats the original message, followed later by a personal reply from the sender.
Objectives of the scam
The full exchange with the sender has been documented, with screenshots and message headers, by Phil Taylor of mySites.guru: Be Aware Of Joomla Developer Impersonation Scams. It shows that the sender pursues two objectives:
-
Administrator access. The recipient is asked to create a Joomla Super User account named "Fotis Evangelou" with the address This e-mail address is being protected from spambots. You need JavaScript enabled to view it , on the pretext of restoring lost access. A Super User account grants full control of a website, including the ability to install extensions, execute code, read the database and create further administrator accounts.
-
Payment. The recipient is offered maintenance plans priced between $350 and $550 and then receives an invoice through a third-party invoicing platform. The invoice is issued under a different name, and the sender asks the recipient not to use the platform's escrow option, which would withhold payment until the work is confirmed.
The messages pass SPF, DKIM and DMARC authentication. These checks confirm only that the messages were sent from that Gmail account. They do not establish who registered the account, and any person can register a Gmail address containing a well-known name.
Verifying correspondence from JoomlaWorks
-
JoomlaWorks and Fotis Evangelou correspond with clients and collaborators only from @joomlaworks.net & @getk2.org. We do not use Gmail or other free email services for this purpose.
-
We do not send unsolicited messages claiming to have been contacted by "Joomla support" about a website.
-
We do not request the creation of Super User or administrator accounts by email, and we do not ask for login credentials to be sent by email.
-
We do not issue invoices through third-party invoicing platforms or under the name of another person.
If you are uncertain whether a message is genuine, do not use any address, telephone number or link it contains. Contact us through a channel you used before the message arrived, or through the contact page on this website.
Recommended action for recipients
-
Do not reply. A reply confirms that your address is active and initiates further contact.
-
Report the message to Google. In Gmail, open the message and select Report phishing. Reports can also be submitted through Google's Gmail abuse form. Multiple reports concerning the same account carry more weight.
-
Delete the message and inform any colleagues who may have received it.
If you have already created an account or made a payment
-
Block or delete the account in Users: Manage, then change the passwords of all Super User accounts.
-
Review the user list for any other Super User or administrator accounts you do not recognise.
-
Review System: Manage: Extensions for recently installed extensions you did not install, and check the User Actions Log for activity by the new account.
-
If the account was used, treat the website as compromised. Restore a known clean backup or have the website audited before returning it to service.
-
If you made a payment, contact your bank or card provider and the invoicing platform immediately and report the transaction as fraudulent.
Reports filed
-
JoomlaWorks has reported the Gmail account to Google as an impersonation, with the full message headers.
-
The Joomla Security Strike Team has confirmed the impersonation and has also reported the account to Google.
-
The fraudulent invoice has been reported to the invoicing platform and its payment processor.
This notice will be updated if further information becomes available.
Other developers affected
According to the mySites.guru report, similar messages are being sent under the names of other well-known members of the Joomla community. We recommend treating any unexpected request for website access or payment with the same caution, regardless of the sender's name, and verifying it through a channel you already trust.
We thank the clients and community members who reported these messages. Please share this notice with anyone who manages a Joomla website.
